Articles
Technical guides, security architecture deep dives, and compliance documentation from the tiCrypt team.
Dynamic Firewall Rules: Implicit and Explicit Network Access for tiCrypt VMs
How VM access rules let chosen VMs reach chosen outside servers, either whenever the VM runs (implicit) or for a limited time after a user opens access (explicit), with examples of each.
Read article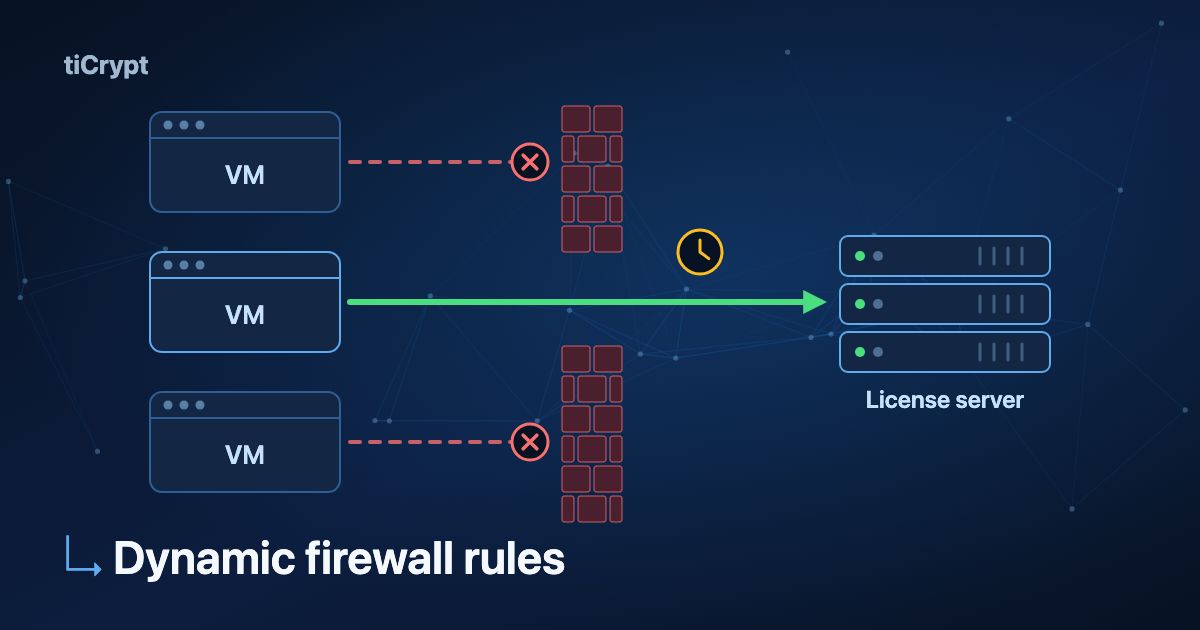
Recent articles
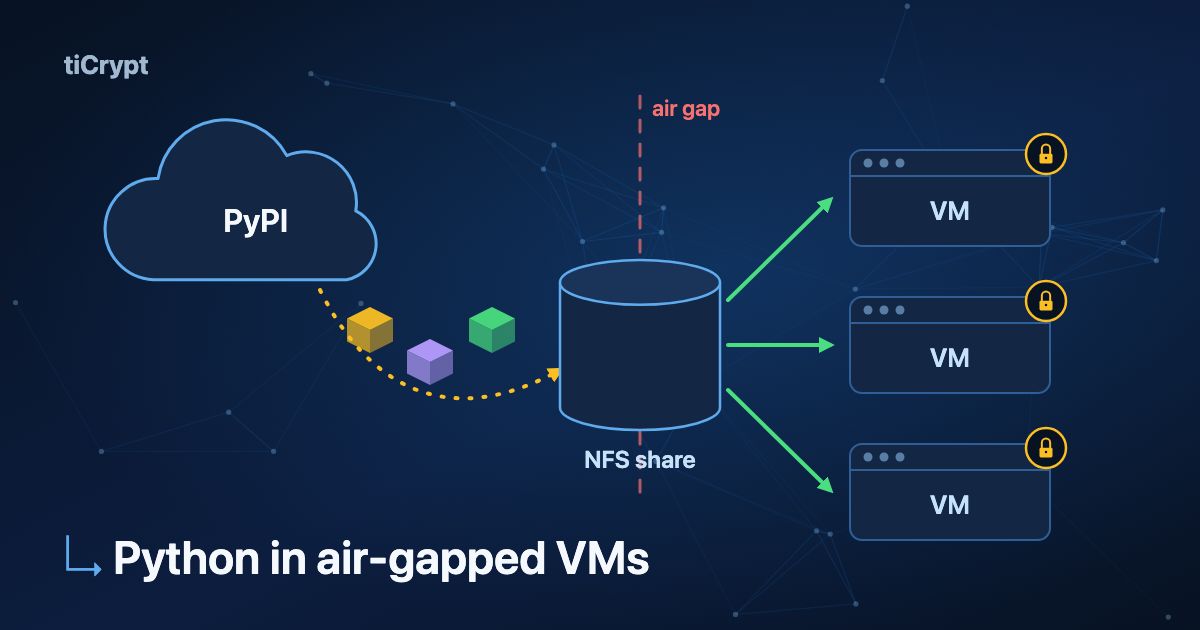
Installing Python Packages in Air-Gapped Research VMs
How tiCrypt's offline PyPI mirror bridges the gap between air-gapped security and researcher access to Python's package ecosystem.
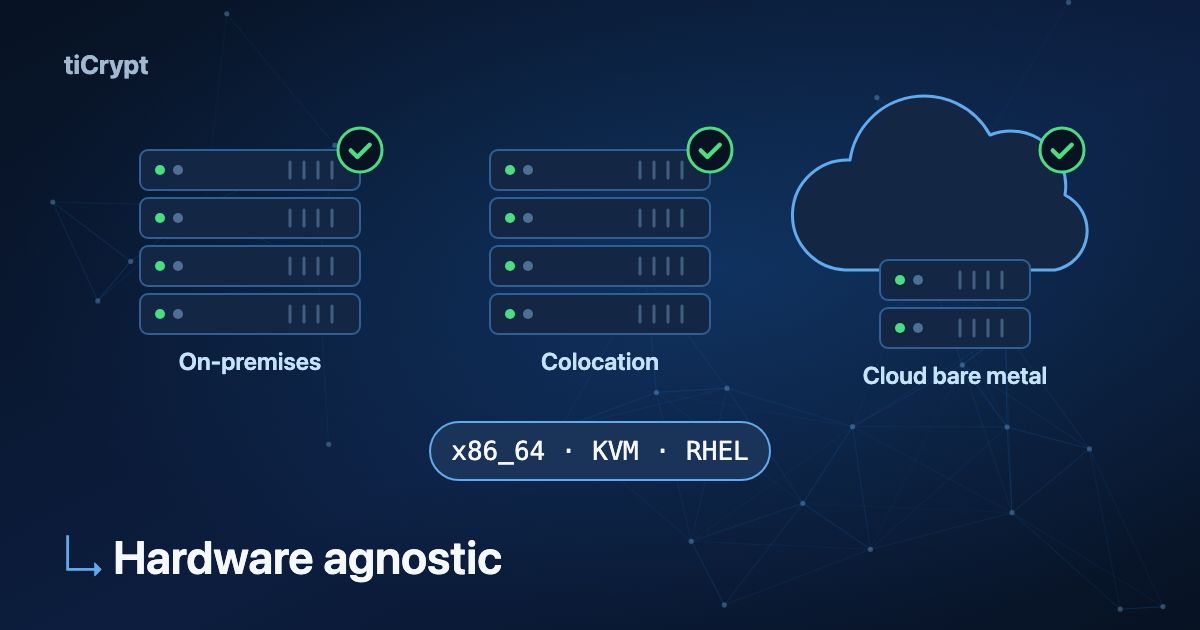
tiCrypt Is Hardware Agnostic: What Actually Matters
What tiCrypt requires from hardware, what affects performance, and what genuinely doesn't matter.
Data Use Agreements: How tiCrypt's Architecture Satisfies Common DUA Requirements
Data Use Agreements impose obligations that most research computing environments cannot structurally guarantee. A clause-by-clause look at how tiCrypt's architecture satisfies the DUA terms compliance officers are asked to sign.
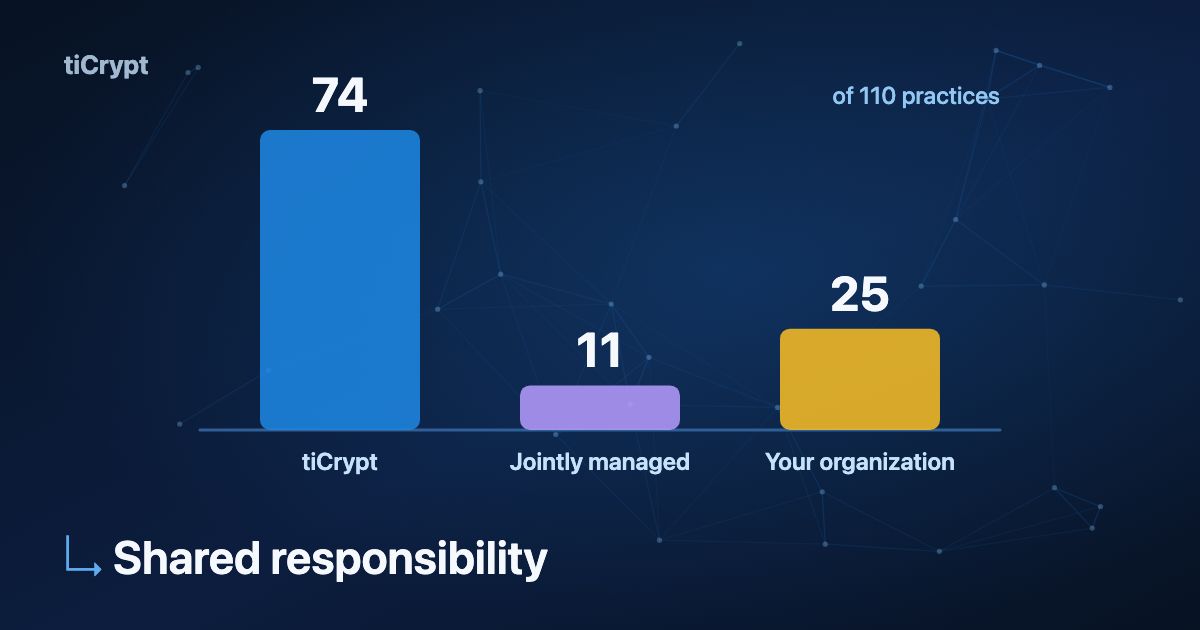
Shared Responsibility in Secure Compute
A control-by-control breakdown of what Tera Insights and tiCrypt handle, what is jointly managed, and what your organization owns across all 110 NIST SP 800-171r2 security practices.
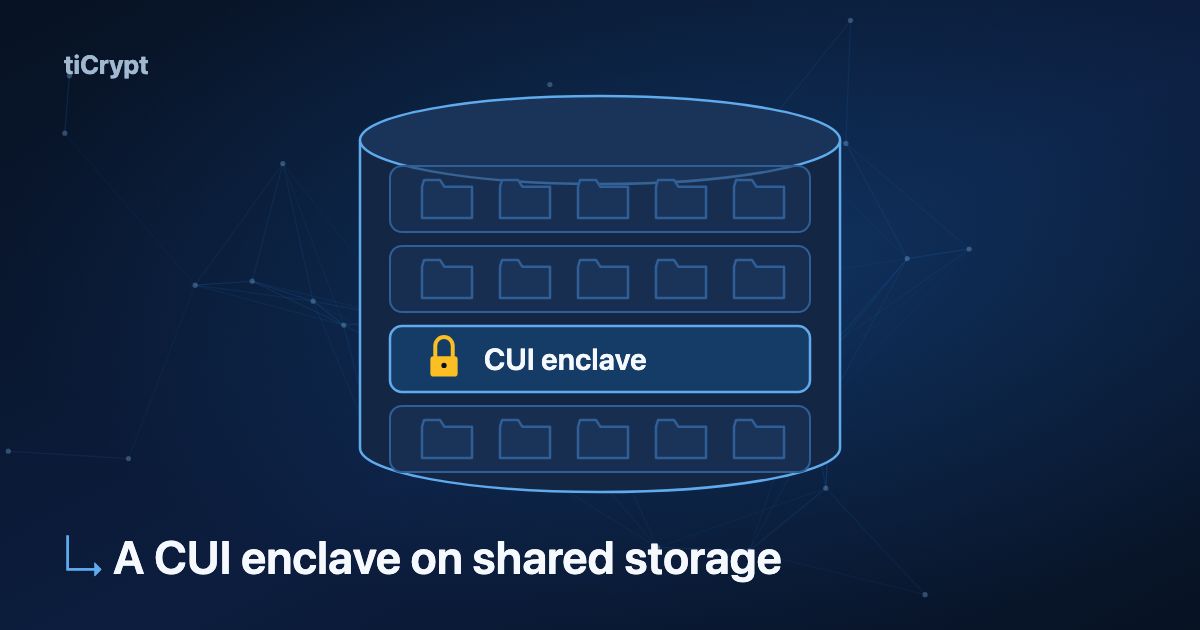
Carving Out a CUI Enclave on Your Existing Filesystem
A technical guide to partitioning shared storage for tiCrypt while maintaining CMMC Level 2 compliance. Covers filesystem requirements, directory structure, permission models, and the CMMC controls that make joint storage acceptable.
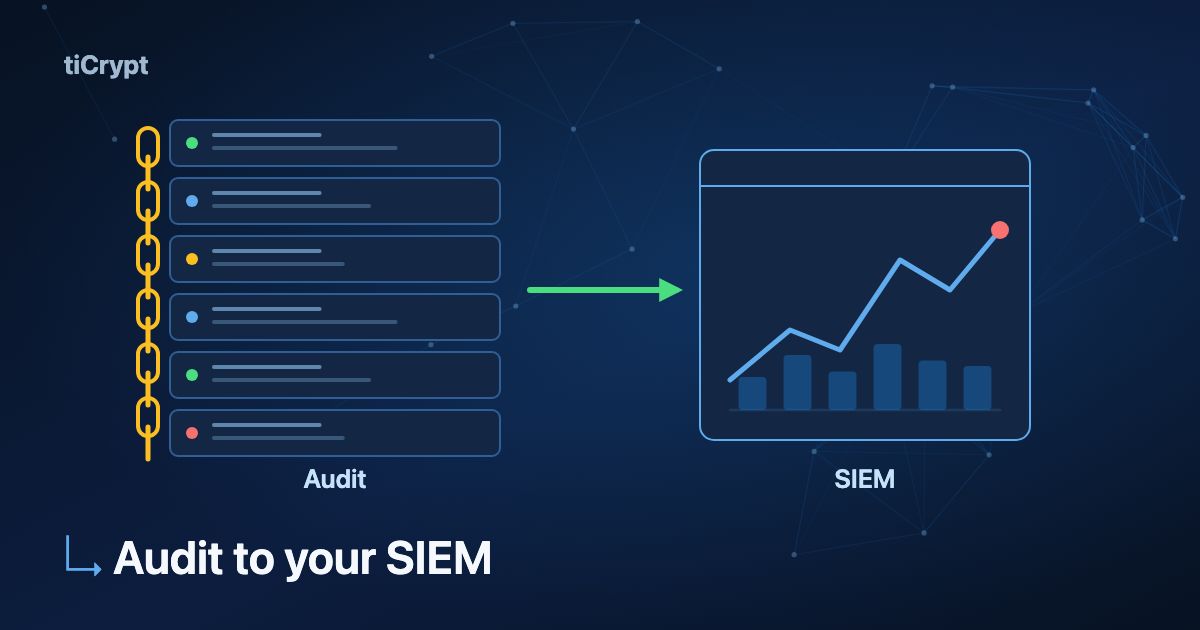
Satisfying CMMC Level 2 Audit and Accountability Controls with tiCrypt
A compliance officer's guide to how tiCrypt satisfies the nine CMMC L2 / NIST SP 800-171r2 Audit and Accountability practices, integrates with your SIEM, and where your organization must supplement with its own controls.